Government Warns Owners About Data Security Vulnerabilities in టాటా మోటార్స్ Apps
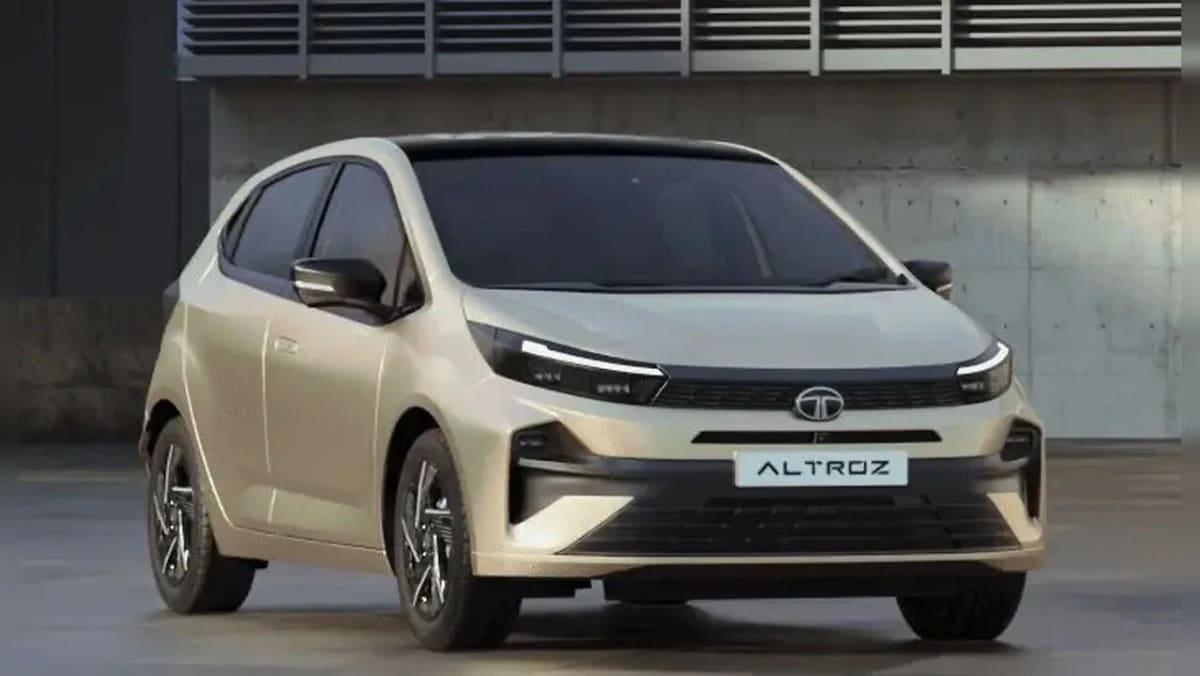
Government cyber security agencies have issued warnings regarding security flaws in connected vehicle applications from టాటా మోటార్స్, prompting calls for user updates.
Government Alerts Drivers Over Connected Vehicle Risks
Indian cyber security authorities have cautioned vehicle owners to secure their connected systems following the discovery of technical flaws in applications provided by టాటా మోటార్స్. Users of these software platforms face potential data privacy risks and unauthorized access to vehicle management tools if their devices remain outdated.
Understanding the CERT-In Advisory
Operating under the Ministry of Electronics and Information Technology, the Indian Computer Emergency Response Team (CERT-In) discovered multiple weaknesses within the connected vehicle mobile utilities. These vulnerabilities could potentially expose private credentials, permit entry into backend operations, misuse authentication tokens, or disrupt communications between the application and its servers.
The advisory impacts individuals utilizing specific software iterations, specifically version 26.7.3 and earlier of the iRA 2.0 platform, along with version 26.7.2 and earlier of the iRA.ev software. Cyber security agencies have urged owners to upgrade their mobile utilities to the newest available software releases immediately to mitigate these threats.
Functionality of the Affected Platforms
The iRA software ecosystem serves drivers of compatible internal combustion engine automobiles and electric vehicles by offering centralized connectivity tools. Through these utilities, operators can check vehicle statuses, review past trip information, and remotely control specific supported vehicle mechanisms. Individuals who heavily rely on these systems for daily management and connected features are encouraged to implement the recommended updates to ensure proper data protection.
Sources: Times Now Telugu, NTV Telugu, Eenadu.
Frequently asked questions
What security issues were found in టాటా మోటార్స్ applications?
Which apps are affected by the CERT-In warning?
What should vehicle owners do to secure their data?
What functions do the affected platforms provide?
Related stories
General Motors Issues Cadillac Blazer Vehicle Safety Recall Over Brakes
General Motors has announced a major safety recall affecting more than 80,000 vehicles, including certain Cadillac and Chevrolet models due to braking concerns.
टोयोटा इनोवा की खोज: ठाणे में 2023 टॉयोटा फॉर्च्यूनर की कीमत और विवरण
टोयोटा इनोवा की खोज के बीच ठाणे में 2023 टॉयोटा फॉर्च्यूनर की कीमत, किलोमीटर और वित्तीय विकल्पों पर विस्तृत जानकारी, साथ ही पुनर्विक्रय संभावनाओं की समीक्षा।

Mahindra Scorpio N Edition One Spied: New Grille and Wine‑Red Cabin Details
Recent sightings reveal the Mahindra Scorpio N Edition One with a refreshed front grille and a wine‑red interior, hinting at an upcoming launch.
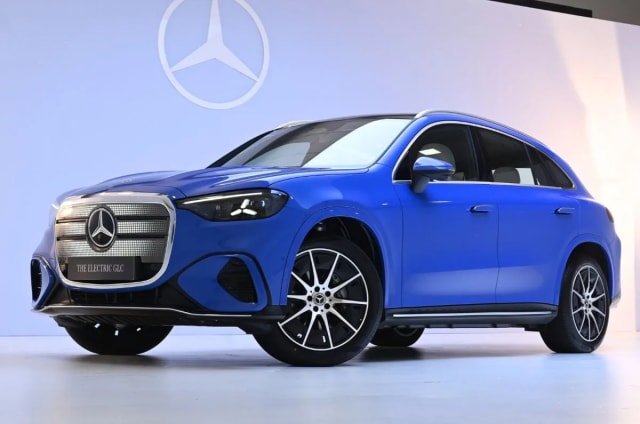
Mercedes-Benz Launches All-New Electric GLC SUV in India Starting at Rs 78.5 Lakh
Mercedes-Benz has introduced its latest electric SUV in India, featuring a massive continuous dashboard screen and a certified range of 711km.